






AI-Native NDR & Network Observability
Vectra
AI-Native Security and Observability
Leader — 2026 Gartner® Magic Quadrant™ for NDR- Attacker-centric AI detects TTPs mapped to MITRE ATT&CK — not just anomalies
- Single platform covering network, identity, SaaS, and public cloud (true hybrid XDR)
- Vectra AI Pro correlates network, identity, cloud, SaaS, EDR and SASE signals for the agentic SOC
Vectra AI is named a Leader in the 2026 Gartner® Magic Quadrant™ for Network Detection and Response
- Recognised as a Leader for the second year in a row
- Positioned highest for Ability to Execute
- Distributed across Africa by Cyber Retaliator Solutions
Hosted by Vectra AI · registration required
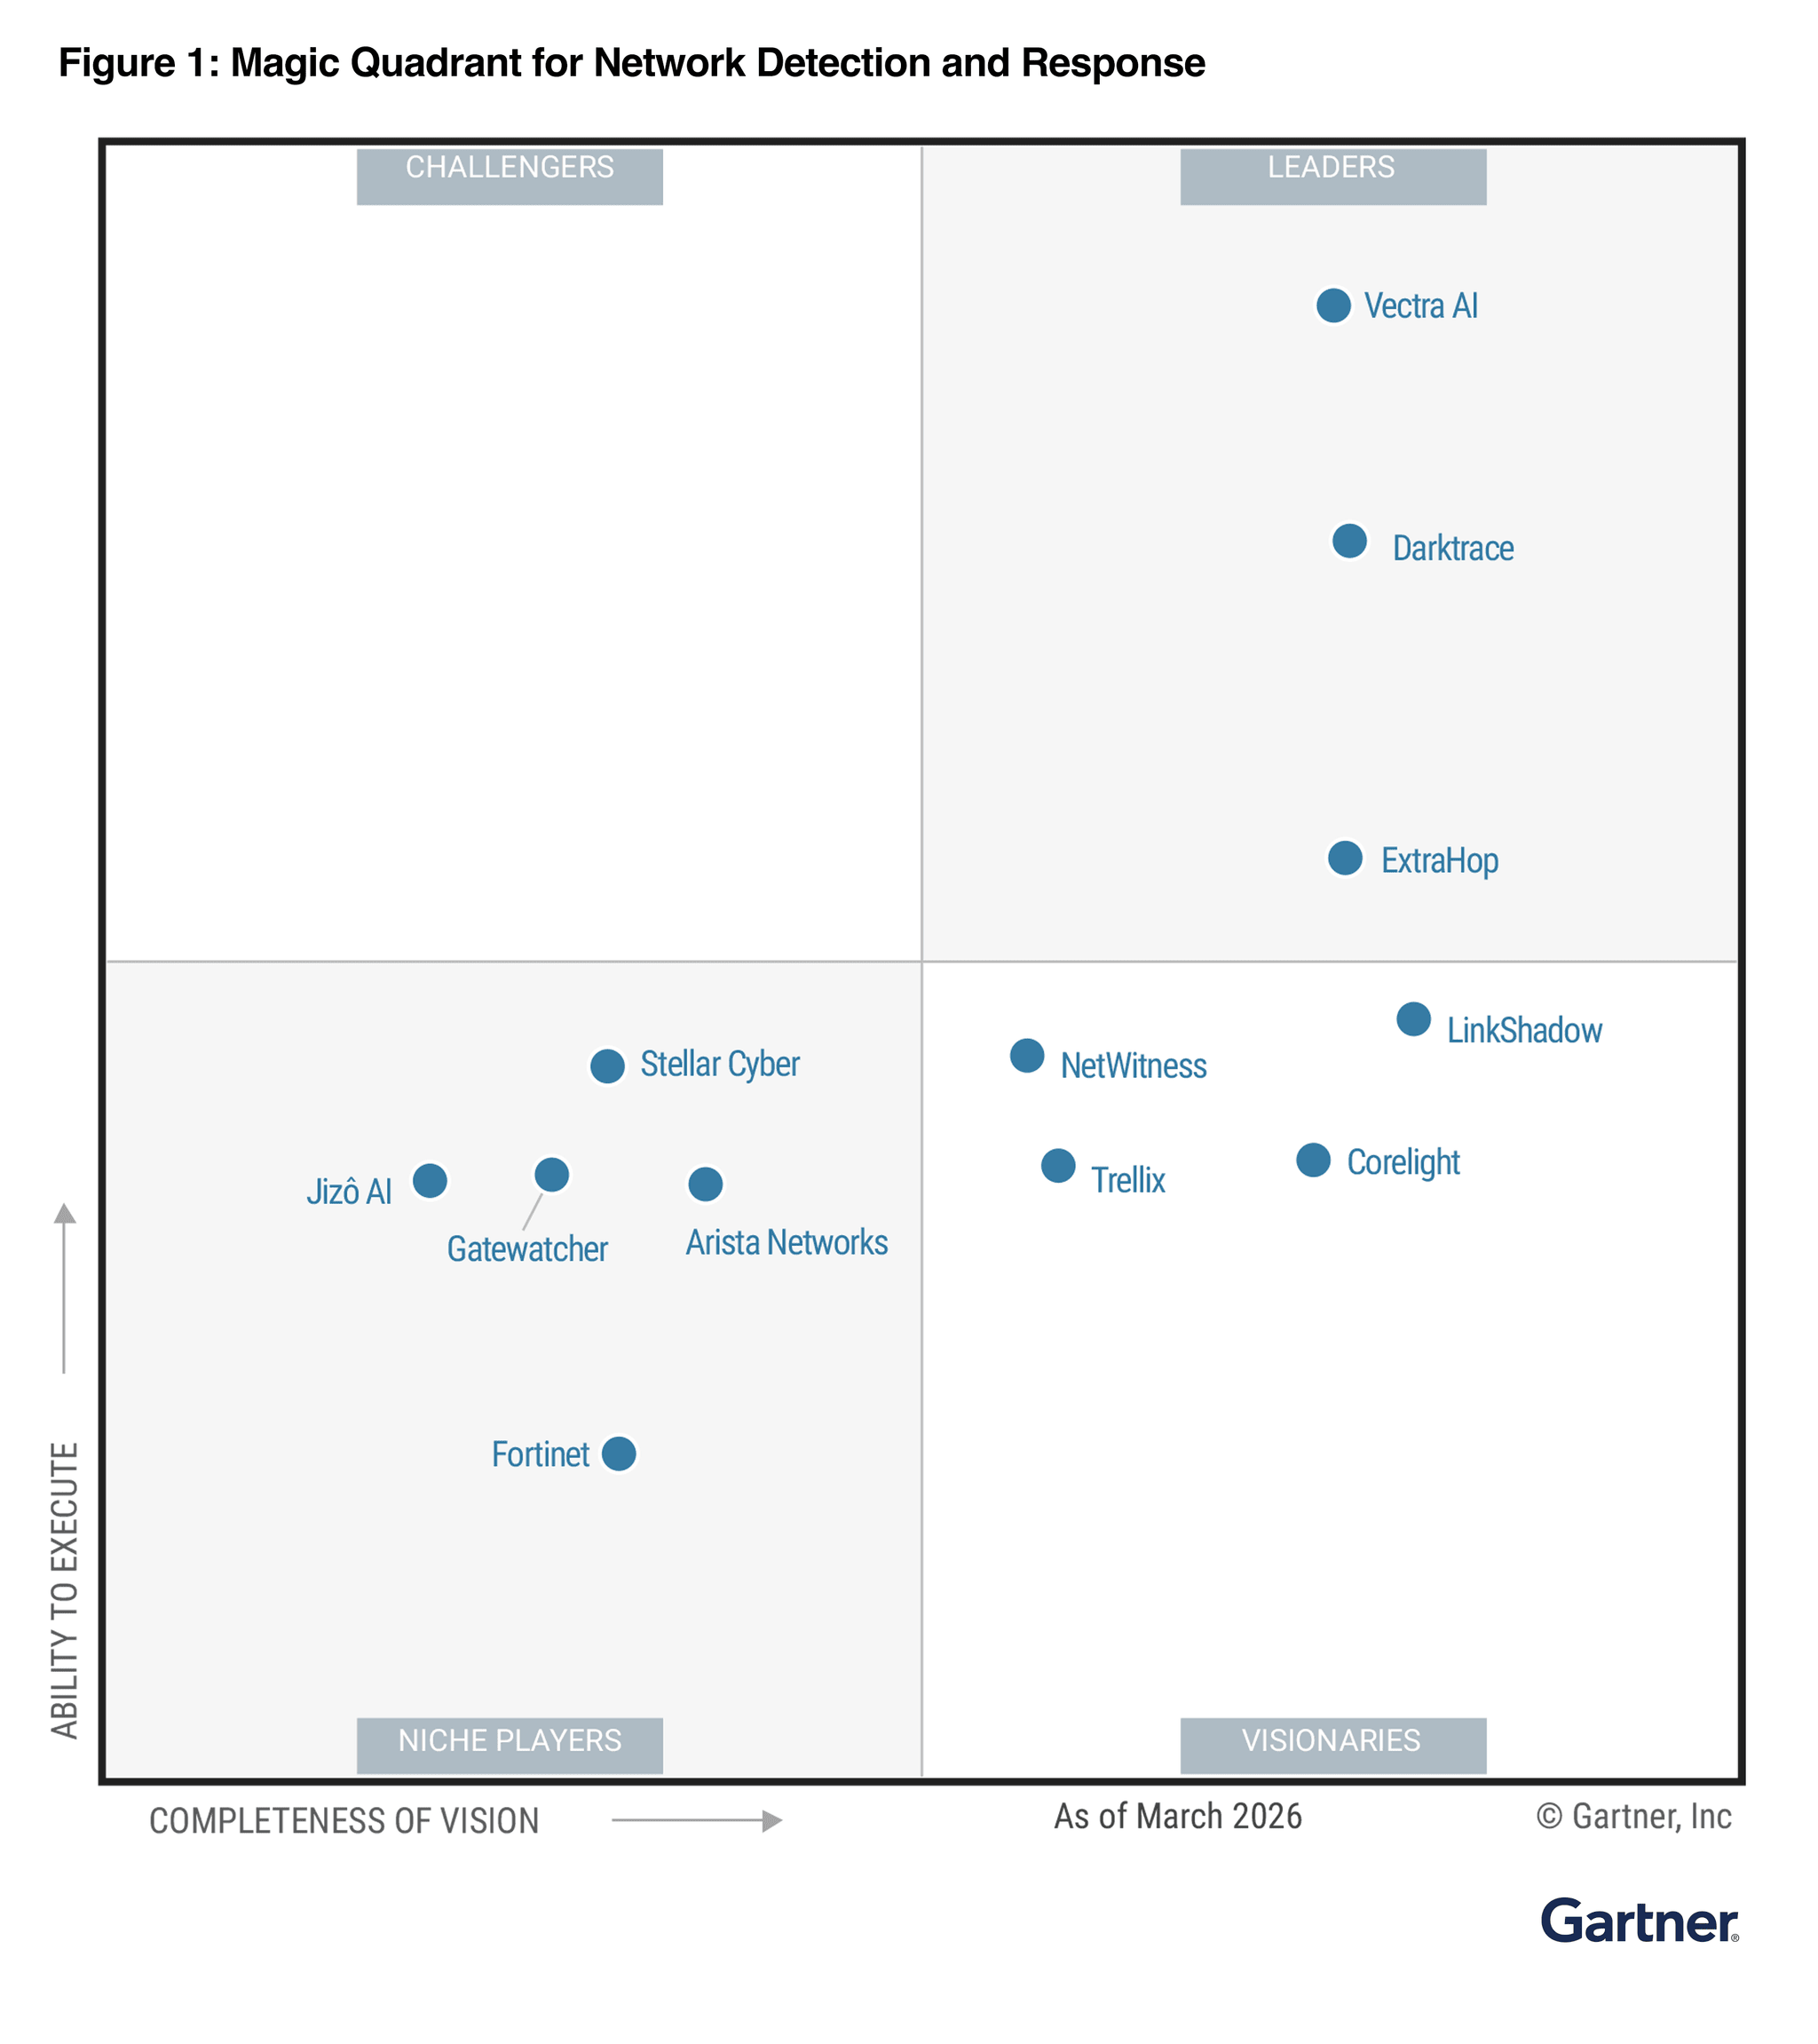
Figure 1: Magic Quadrant for Network Detection and Response — as of March 2026 © Gartner, Inc.
Gartner®, Magic Quadrant™ for Network Detection and Response, March 2026. This graphic was published by Gartner, Inc. as part of a larger research document and should be evaluated in the context of the entire document.
Gartner does not endorse any vendor, product or service depicted in its research publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner's research organisation and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose. GARTNER is a registered trademark and service mark, and MAGIC QUADRANT is a registered trademark, of Gartner, Inc. and/or its affiliates in the U.S. and internationally. All rights reserved.
Hybrid AI Detection and Response
Vectra AI detecting real attacker behaviour across network, identity, SaaS, and cloud — with the noise stripped out before it reaches an analyst.
Overview
Vectra is the leader in AI-driven threat detection and response for hybrid and multi-cloud enterprises. Vectra's patented Attack Signal Intelligence™ detects and prioritises threats across public cloud, SaaS, identity, and networks in a single platform. Founded in 2011, Vectra holds 39 patents in AI-driven threat detection, covers >90% of MITRE ATT&CK techniques, and serves 2,000+ organisations with a 95% retention rate. The platform now spans three pillars — network observability, threat detection and response, and network exposure management — and is named a Leader in the 2026 Gartner® Magic Quadrant™ for Network Detection and Response.
Who It's For
Key Differentiators
- Attacker-centric AI detects TTPs mapped to MITRE ATT&CK — not just anomalies
- Single platform covering network, identity, SaaS, and public cloud (true hybrid XDR)
- Vectra AI Pro correlates network, identity, cloud, SaaS, EDR and SASE signals for the agentic SOC
- Vectra Fusion adds agentless multi-cloud network observability across AWS, Azure, GCP and Oracle Cloud
- Network Exposure Management with continuous asset inventory — finds unmanaged, OT and IoT devices
- Cloud Detection & Response for AWS, Azure and Microsoft 365, including Microsoft Copilot coverage
- Agentless deployment — network coverage live in days, cloud in hours
- Reduces SIEM alert volume and detection rule maintenance overhead significantly
- Automates analyst investigation tasks and accelerates Mean Time to Respond (MTTR)
- Optimises existing EDR, SOAR, and ITSM investments via 40+ pre-built integrations, an MCP server and the CrowdStrike Marketplace
- 3 Global SOCs with 60+ MDR analysts for 24x7x365 managed detection and response
- 95% customer retention rate — proven enterprise outcomes
- Priced on concurrent IPs, internal accounts, or AWS flow data (not per-agent)
Competitive Positioning
vs. Darktrace
- ›Vectra detects attacker TTPs (MITRE ATT&CK) — Darktrace flags anomalies which generates far more false positives
- ›Higher-fidelity detections mean analysts chase real threats, not noise
- ›Vectra covers hybrid environments (cloud, SaaS, identity) — Darktrace is primarily network-only
- ›Vectra Attack Signal Intelligence™ provides explainable AI — Darktrace's 'self-learning AI' is a black box
vs. ExtraHop
- ›Vectra extends to SaaS, identity (Azure AD/M365), and public cloud — ExtraHop is network-only
- ›Vectra includes MDR service; ExtraHop requires separate SOC engagement
- ›Vectra requires no additional analyst tuning — ExtraHop demands significant rule customisation
vs. Corelight
- ›Vectra delivers AI-driven detection + response out of the box — Corelight is raw log/packet capture only
- ›Corelight requires a SIEM and analyst team to derive value; Vectra works standalone
- ›Vectra covers identity and cloud; Corelight is network traffic analysis only
vs. IDS / Suricata
- ›Vectra requires zero signature rule maintenance — IDS is entirely signature-based
- ›Vectra detects unknown and zero-day attack patterns; IDS only detects known signatures
- ›Vectra covers cloud and SaaS attack surfaces; IDS/Suricata is perimeter-only
vs. LinkShadow
- ›Vectra covers hybrid environments end-to-end — network, identity (Active Directory / Azure AD), SaaS (M365), and public cloud (AWS/Azure/GCP) in one platform; LinkShadow is primarily on-premises network traffic analysis
- ›Vectra's patented Attack Signal Intelligence™ maps detections directly to MITRE ATT&CK TTPs with full explainability — LinkShadow uses black-box behavioural ML with limited analyst context for prioritisation
- ›Vectra includes 3 Global SOCs with 60+ MDR analysts for 24/7 managed detection and response; LinkShadow has no comparable managed service — customers must bring their own SOC
- ›Vectra is named a Leader in the 2026 Gartner® Magic Quadrant™ for Network Detection and Response, for the second year in a row — LinkShadow has no comparable independent analyst recognition at enterprise scale
- ›Vectra integrates natively with 40+ SOAR, SIEM, EDR, and ITSM platforms — LinkShadow has limited third-party ecosystem depth, creating analyst workflow gaps
- ›Vectra serves 2,000+ organisations with a 95% retention rate — proven at scale in complex hybrid environments where LinkShadow is typically deployed in simpler on-premises-only estates
Full partner battle cards, pricing intelligence, and objection-handling guides available in the partner portal.
Partner Use Cases
Replacing Legacy IDS for a Financial Services Client
An MSSP partner replaces a client's ageing Suricata-based IDS with Vectra AI across a hybrid on-premises and Azure AD environment. Vectra's agentless deployment goes live in days, immediately surfacing lateral movement and privilege escalation activity that the IDS missed entirely. The partner delivers MITRE ATT&CK-mapped detection reports as quarterly compliance evidence for PCI DSS — turning an existing security gap into a new managed NDR service line.
Reducing SIEM Alert Fatigue for an Overwhelmed SOC
A partner's enterprise client is drowning in tens of thousands of daily SIEM alerts with a two-analyst team. By layering Vectra AI on top of the existing SIEM, the partner reduces actionable alert volume dramatically — Vectra's AI surfaces only the detections that require analyst investigation. The SOC reclaims capacity to investigate real threats rather than triaging noise, and the partner upsells a Vectra MDR co-management arrangement.
Extending MDR with 24/7 SOC Coverage Under a Partner Brand
A regional MSSP lacks the headcount to offer 24/7 detection and response. By reselling Vectra's MDR service — backed by Vectra's three global SOCs and 60+ dedicated analysts — the MSSP extends its service catalogue to include enterprise-grade managed detection across network, identity, SaaS, and cloud without additional internal headcount. The partner earns a margin on the Vectra MDR subscription and retains the client relationship.
Want to walk through one of these scenarios against your own environment? Request a demo or speak to a CRS specialist.
Webinars & Articles
Go deeper on Vectra with sessions and write-ups from the CRS team.
Frequently Asked Questions
How does Vectra's Attack Signal Intelligence™ differ from traditional SIEM detection?
SIEM detects based on predefined rules and log correlation — it requires continuous tuning and generates high volumes of false positives. Vectra's Attack Signal Intelligence™ uses AI trained on real attacker behaviours to detect Tactics, Techniques, and Procedures (TTPs) mapped to MITRE ATT&CK across network, identity, SaaS, and cloud — without signature rules. This surfaces only the detections that require analyst action, significantly reducing noise while increasing fidelity.
Does Vectra replace our existing EDR?
Vectra complements rather than replaces EDR. EDR provides endpoint-level telemetry and response; Vectra provides network, identity, SaaS (M365), and cloud attack surface coverage that EDR cannot see — lateral movement over the wire, Azure AD account compromise, and cloud workload threats. Together they form a complete XDR picture. Vectra integrates natively with CrowdStrike, SentinelOne, and Microsoft Defender via 40+ pre-built integrations.
What environments does Vectra monitor?
Vectra monitors on-premises networks (via network sensors), Microsoft Azure AD and M365 (agentless via API), AWS cloud (via VPC flow logs), GCP, and SaaS applications — all in a single unified platform covering more than 90% of MITRE ATT&CK techniques. This makes it the only platform providing true hybrid XDR across network, identity, SaaS, and public cloud.
How quickly can Vectra be deployed and deliver value?
Network coverage is live within days of sensor deployment; cloud and M365 coverage can be active within hours via agentless API integration. Vectra requires no signature rule writing and no extended tuning baseline — detections are active immediately, making it one of the fastest-to-value NDR platforms available.
What does the Vectra MDR service include?
Vectra MDR is a 24×7×365 managed detection and response service operated by Vectra's three global SOCs with 60+ dedicated analysts. MDR analysts triage Vectra AI detections, investigate incidents, and escalate confirmed threats directly to your security team via your preferred channel. Vectra MDR covers network, identity, SaaS, and cloud — providing full hybrid environment managed coverage.
Partner Intelligence Available
Partner pricing, discount tiers, detailed battle cards, and full sales enablement content for Vectra are available exclusively to authorized CRS partners.
Your Vectra lead
 Tate Tichiwangana
Head Security Engineer
Best for: POC phases, technical deep dives, and solution validation cycles where accuracy and speed matter.
Book a meeting with Tate
Opens Tate's calendar in a new tab.
Request a DemoBecome a CRS Partner
Get exclusive partner pricing, sales tools, and enablement resources for Vectra.
Apply for Access Partner Sign InBuild the Skills
Equip your team to deploy and manage Vectrawith CRS authorized IBM, Red Hat, SUSE & CompTIA technical training.
Explore CRS technical trainingVendor Website
vectra.aiRequest a Demo of Vectra
Tell us what you need and when works for you — a member of the CRS team will confirm your session directly.
More in Threat Detection & Response
Products CRS partners commonly position alongside Vectra.